Smart manufacturing systems face critical cybersecurity risks as production equipment connects to the cloud, exposing operational data to attackers who exploit weak network segmentation and unpatched systems. Manufacturers must implement OT security assessments, network segmentation, and multi-factor authentication to bridge IT and OT security gaps.
- Four top vulnerabilities in smart manufacturing include flat network architectures, legacy equipment without security controls, unpatched cloud gateways, and unsecured third-party remote access.
- Network segmentation is critical—separate OT networks from IT networks using firewalls and VLANs to limit lateral movement by attackers.
- Remote access control requires multi-factor authentication (MFA) and time-limited credentials for machine builders and integrators accessing equipment.
- Continuous monitoring with OT-aware intrusion detection systems (IDS) helps detect unusual behaviors like changes to machine logic or suspicious data spikes.
- Shared responsibility between IT and OT teams, plus cybersecurity documentation from OEMs, are essential for protecting connected manufacturing operations.
Smart manufacturing is here, and it’s accelerating. Connected packaging machines, IIoT sensors, remote monitoring platforms, and cloud analytics tools are transforming the way the packaging and processing industry operates. Real-time data is reducing downtime, predictive maintenance is improving uptime, and machine insights are driving productivity gains on the line.
But with these gains comes a significant risk: Your operational data is more exposed than ever before.
Cybercriminals are shifting their focus from traditional IT systems to operational technology (OT) — and manufacturers that haven’t secured both are finding themselves vulnerable in places they didn’t expect.
When “Air-Gapped” isn’t air-tight
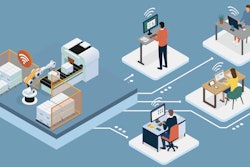
Many manufacturers assume their production environments are isolated. But modern packaging and processing lines increasingly connect to the cloud — for remote diagnostics, firmware updates, and real-time performance dashboards. That convenience can blur the line between IT and OT.
And if a malicious actor gains access through a weakly secured vendor integration or unmanaged sensor connection? They might:
- Exfiltrate sensitive production data.
- Disrupt machine operations.
- Deliver ransomware that halts your entire line.
Fact: In recent attacks, hackers have pivoted from HVAC system controllers to critical OT systems — all because the networks were improperly segmented.
The four top vulnerabilities in smart manufacturing
- Flat Network Architectures - Many OT systems were never designed with network segmentation in mind. Once breached, attackers can easily move laterally across the network to other devices.
- Legacy Equipment with No Security Controls - Older PLCs and control systems often lack basic protections like authentication or encryption.
- Unpatched Cloud Gateways - Edge devices and cloud connectors may not receive updates — creating a soft underbelly for attackers. This can be especially true at remote production sites with connectivity challenges or older networking equipment.
- Third-Party Remote Access - Machine builders and integrators often need remote access to equipment, but unsecured VPNs or shared logins are a common weakness.
Bridging the IT/OT cyber gap
Cybersecurity in smart manufacturing is no longer just about protecting office systems. It's about creating shared accountability between IT and OT teams — and building security into every level of your technology stack.
Here’s how the industry can take proactive steps:
1. Conduct an OT Security Risk Assessment - Map out all devices connected to your production networks. Identify data flows between machines, cloud platforms, and external vendors.
2. Implement Network Segmentation - Separate OT networks from IT networks using firewalls, VLANs, wireless connectivity, or other technologies. Limit what each “segment” can access.
3. Control Remote Access - Require multi-factor authentication (MFA) for remote vendor access. Use logging tools and time-limited credentials if possible.
4. Keep Software and Firmware Updated - Patch not just your laptops, but also your machine interfaces, sensors, and industrial controllers when updates are available.
5. Monitor for Anomalies - Use OT-aware intrusion detection systems (IDS) to spot unusual behaviors, like changes to machine logic or data spikes.
The role of OEMs and solution providers
If you build or integrate machines, your role in cybersecurity is more important than ever. Provide your customers with cybersecurity documentation, recommended configurations, and update schedules. Consider offering secure remote access as a service, with controls that meet NIST or other cybersecurity standards.
A call to action
As the line between physical equipment and digital data continues to blur, so does the line between convenience and vulnerability. Whether you're a CPG manufacturer or a machinery supplier, the new reality is this:
Every machine is now a potential data leak or attack vector — unless you secure it.
Cybersecurity isn’t just an IT concern anymore. It’s a business continuity issue, a safety issue, and a brand protection issue. It’s everyone’s responsibility!